Features Quick Demo Pricing Trust Center Docs Whitepaper Install VS Code Extension Schedule Demo →

Use ChatGPT, Claude, Copilot at work. Without the guilt.

SecureAIFlow strips API keys, secrets, and PII from your prompts before they leave your IDE. Self-hosted on your infrastructure. GDPR & DORA ready.

Self-hosted Your infrastructure Full control

How your prompts flow

Your IDE / Browser
apiKey = "sk-abc..."
→
SecureAIFlow
EU · in-memory · no storage
→
Claude · GPT · Gemini
apiKey = "[REDACTED_1]"

Your prompts never touch disk. Redaction happens in memory, in Germany, in milliseconds. Nothing is stored, nothing is trained on.

Recognized by

Google for Startups
OWASP GenAI Security
Live Now · VS Code Marketplace

Secrets redacted before they leave your IDE

API keys, credentials, and tokens are detected and replaced with pseudonyms directly in your VS Code workflow. Chat, refactor, explain — sensitive data never reaches OpenAI, Anthropic, or Google.

Install from VS Code Marketplace →
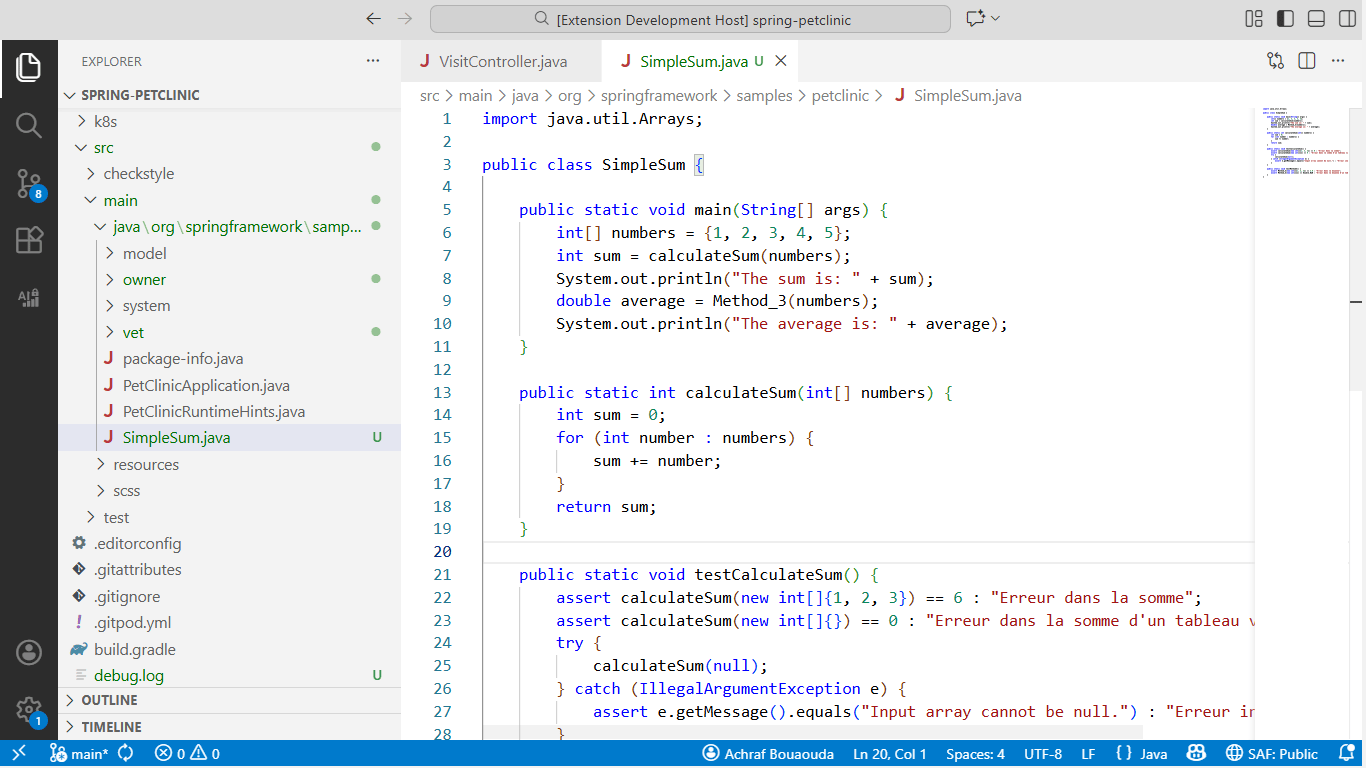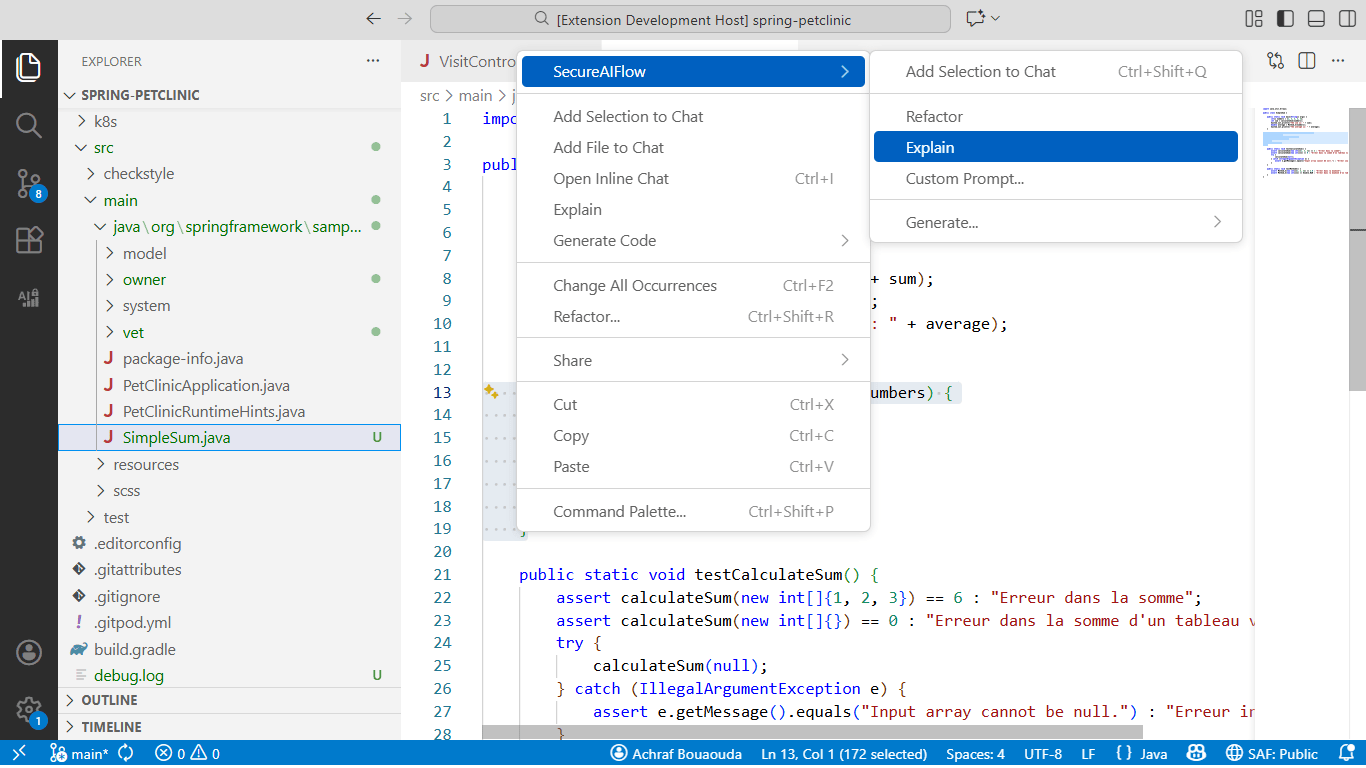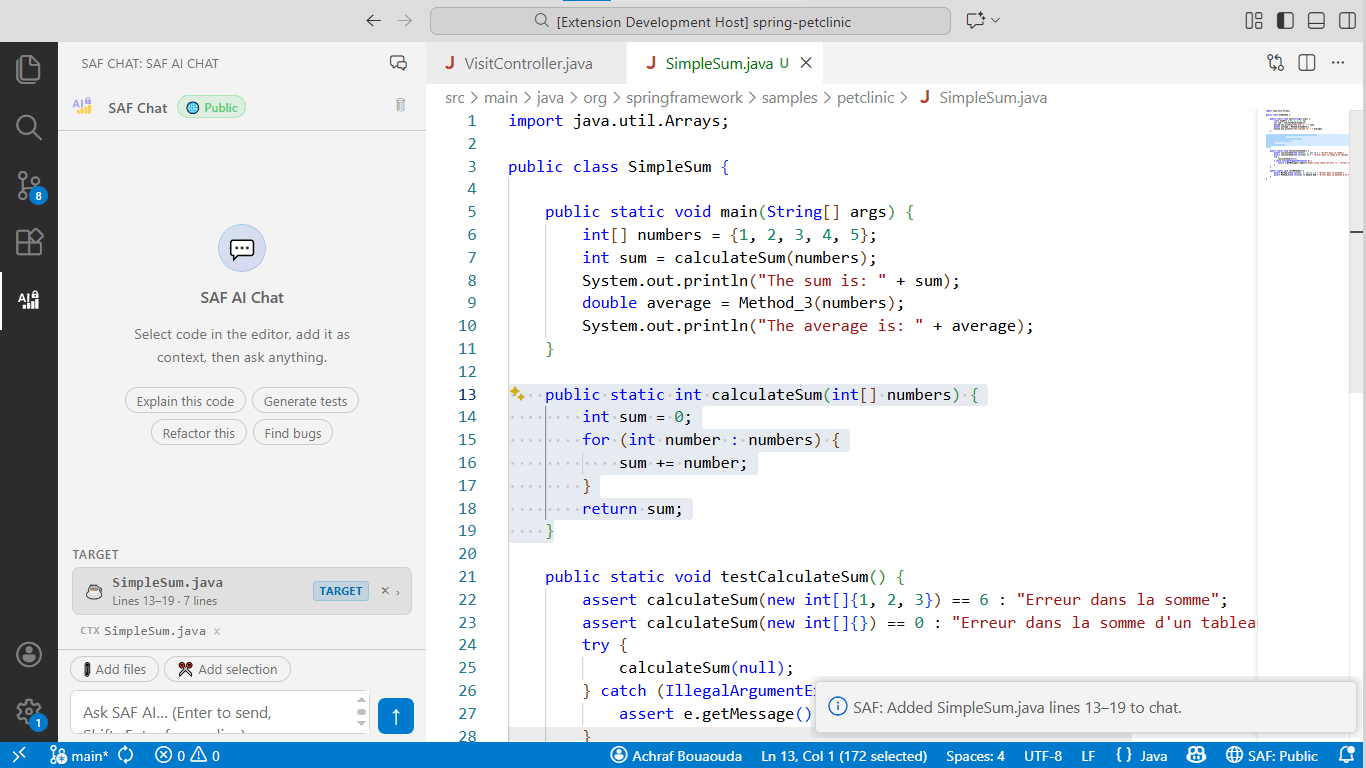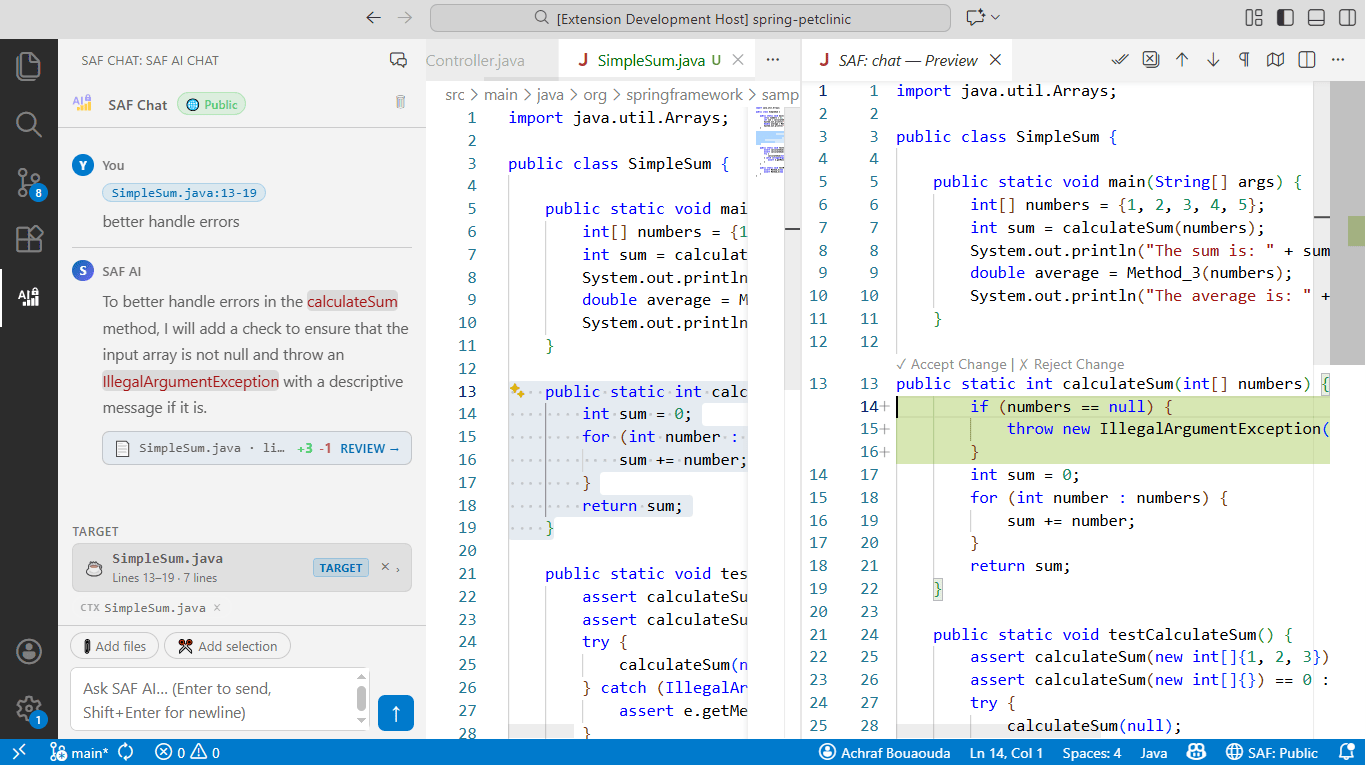
VS Code Extension Demo
New · Terminal-first

Claude Code, proxied. Zero config.

Two environment variables — no install, no code change. SecureAIFlow proxies every Claude Code request through the redaction engine. Bash outputs, file reads, and tool_results are sanitized before reaching Anthropic. Bring your own Anthropic key, keep your audit trail.

See the setup →
# 1. Point Claude Code at SecureAIFlow
export ANTHROPIC_BASE_URL=https://api.secureaiflow.com
export ANTHROPIC_CUSTOM_HEADERS="x-saf-user: you@co.com"
# 2. Use Claude Code as usual
$ claude "fix the failing auth tests"
↳ tool_result · cat .env
DB_PWD=prod-s3cret!2026
DB_PWD=[REDACTED_1] ✓ sent to Anthropic
For Leadership

Full visibility — the control plane your CISO wants

Secrets caught, tokens scanned, cost per LLM provider, team activity. Every AI interaction tracked and measured — with a full audit trail that satisfies DORA Article 28 and GDPR requirements.
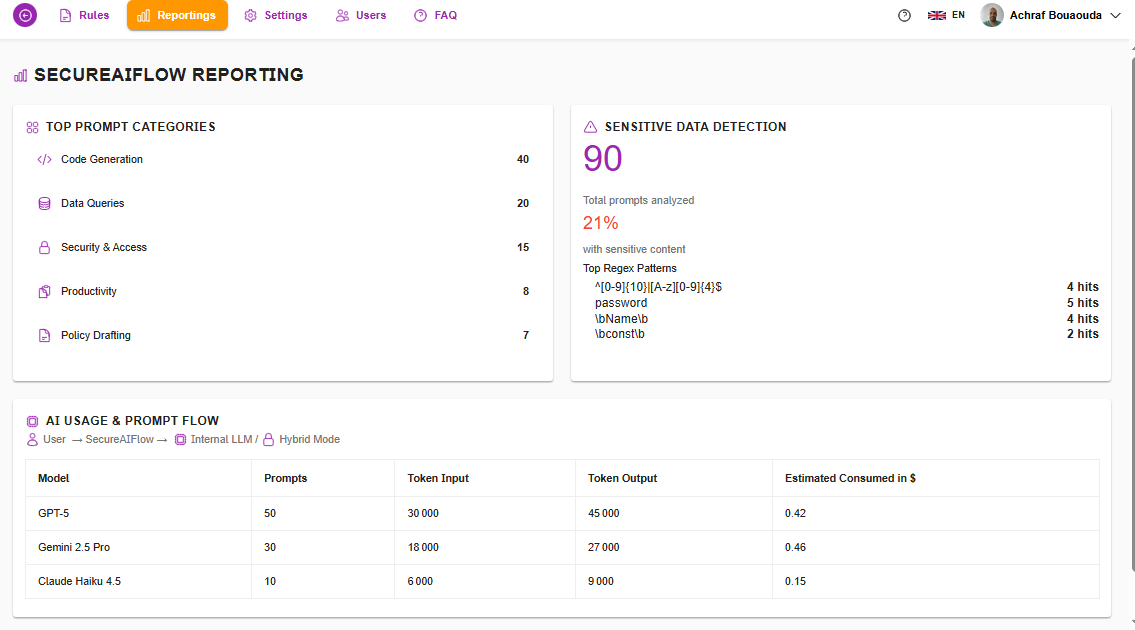
Dashboard Screenshot

Watch how SecureAIFlow protects your team

A 2-minute walkthrough of how SAF intercepts, redacts, and governs every AI interaction.

97%
F1-score
3-Stage
Hybrid detection pipeline
Zero
Prompt storage · in-memory only
DORA
Compliant · Article 28 ready

Every AI prompt is a potential data leak

API keys, credentials, PII — pasted into ChatGPT, Copilot, and every AI tool. You can't block AI. Your devs will use it anyway. You need to secure it.

Without SecureAIFlow
  • ✕API keys sent to ChatGPT in plain text
  • ✕Customer PII shared with AI models
  • ✕No visibility on what's leaving your org
  • ✕DORA Article 28 & GDPR exposure
  • ✕Devs use personal accounts to bypass IT
With SecureAIFlow
  • +Secrets detected and redacted in real-time
  • +PII pseudonymized before reaching any LLM
  • +Full audit trail of every AI interaction
  • +GDPR & DORA compliant from day one
  • +Devs keep using their favorite AI tools

Three steps. Secrets stay yours.

SAF sits between your teams and every AI tool they use.

01

Intercept

The VS Code extension , Chrome plugin and web chat capture prompts before they leave your environment.

02

Detect & Redact

Three-stage hybrid pipeline (regex + fine-tuned MiniLM + deterministic pseudonymization) reaches F1 0.97. Connect your vault for 100% coverage.

03

Route to LLM

BYOK mode sends to your provider. Smart Routing intelligently routes across Claude, GPT-5, and Gemini based on complexity and cost.

On-Premises Only

Self-hosted security layer deployed on your infrastructure. Complete control, full compliance, custom pricing.

Ready to secure your enterprise?

Self-hosted deployment · Complete control · Full compliance